
Nordstern Intelligence Hub
In-depth threat analysis, compliance guides, and tactical strategies to protect your business operations. Authored directly by our elite SOC engineers.
The penetration test PCI requires (Req. 11.4), and what an ASV scan does not cover
Four passing ASV scans do not satisfy Requirement 11.4. They satisfy Requirement 11.3.2,…
Read more
What PCI DSS compliance actually costs, and what drives the number
Nobody can quote you a PCI DSS compliance cost from the name of…
Read more
The PCI DSS checklist that survives a QSA
Most PCI checklists are the twelve requirements retyped with tick boxes next to…
Read more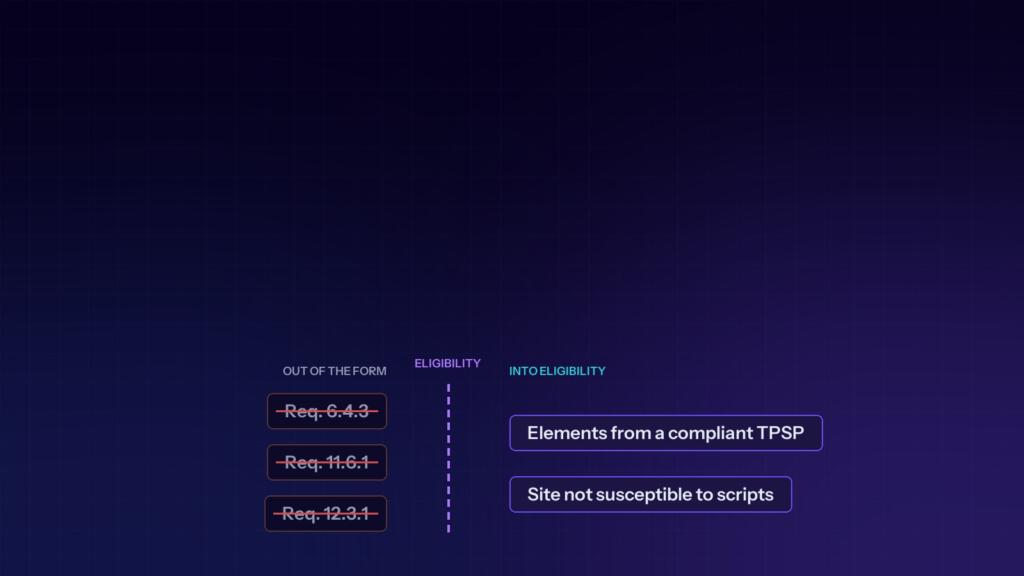
SAQ A in 2026: the eligibility line that moved, and who now falls outside it
Your payment provider tells you that SAQ A still covers you. Your assessor…
Read more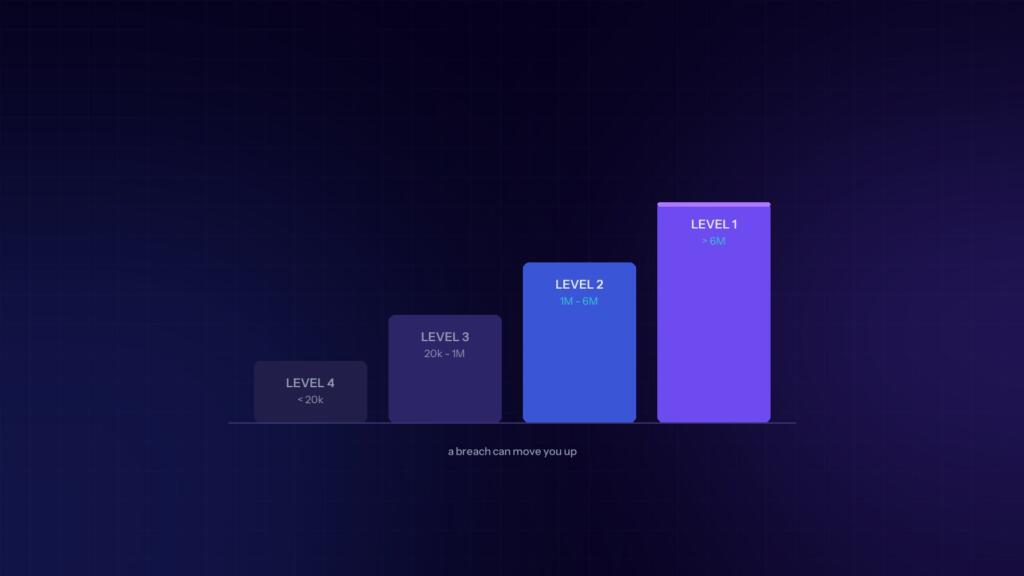
PCI merchant levels: how your level is set and what it changes
Your level is not set by the PCI Council. Visa and Mastercard each set their own, your acquirer tells you,...
Read more
Incident response plan template: what to write in each section
Most incident response plans are written for an auditor and read for the…
Read more
ISO 27001 certification: the real process, the evidence, and how long it takes
A customer asks for “your ISO 27001 accreditation” before signing. Someone forwards the…
Read more
What an Approved Scanning Vendor (ASV) does, and how to pass your quarterly PCI scan
Your acquirer asks for a passing scan every quarter. Your scanning tool says…
Read more